We're excited to announce the release of react-native-auth0 v6.0.0!
For v6.0.0 users: This version is New Architecture-only and requires React Native 0.82+ (Expo SDK 55+), Android API 26+, and JDK 17. See the 👉 Migration Guide 👈 for compatibility requirements and upgrade instructions.
This SDK targets apps that are using React Native SDK version 0.82.0 and up. If you're using an older React Native version, stay on an earlier release of this SDK (see below).
This SDK is New Architecture-only — the Legacy Architecture is no longer supported. React Native 0.82 is the first release to run entirely on the New Architecture; as of v6, this SDK requires React Native 0.82+. If your app has not yet moved to the New Architecture, upgrade to 0.82+ or stay on v5.x.
⚠️ Warning: For Expo, this version requires Expo SDK 55 or higher (Expo 54 ships React Native 0.81, below the 0.82 floor). If you are on an earlier Expo version, upgrade Expo or stay on react-native-auth0 5.x (Expo 53–54) or 4.x (below Expo 53).
Platform compatibility
The following shows platform minimums for running projects with this SDK:
Platform
Minimum version
iOS
15.1
Android
API 26 (Android 8.0)
iOS. This SDK requires a minimum iOS deployment target of 15.1, inherited from the React Native 0.82+ Pods (min_ios_version_supported). In your project's ios/Podfile, set the platform accordingly — following the older 14.0 value will fail pod install:
platform :ios, '15.1'
Android. This SDK requires minSdkVersion 26 (Android 8.0). It compiles against compileSdkVersion 36 and must be built with JDK 17. Raise these in your app's android/build.gradle (and verify your toolchain with java -version) if you are coming from an earlier setup. See the Migration Guide for details.
The iOS pod ships a privacy manifest (PrivacyInfo.xcprivacy) that declares no tracking, no required-reason API usage, and a user identifier collected only for app functionality. Xcode includes it automatically when you generate a privacy report, so you don't have to describe this SDK's behavior yourself. You are still responsible for reviewing that report and for keeping your App Store Connect privacy answers accurate for your app as a whole, including the data this SDK collects.
Then, you need to run the following command to install the ios app pods with Cocoapods. That will auto-link the iOS library:
$ cd ios && pod install
iOS framework linkage (use_frameworks!)
This SDK's native dependencies — Auth0 3.3.1, JWTDecode 4.0.0, and SimpleKeychain 1.3.0 — are Swift pods. They install with the default React Native static-library linkage (no use_frameworks!), so most apps need no extra Podfile changes.
If your project requires use_frameworks! (for example, because another dependency ships as a framework), both linkage modes are supported — this was verified by building the example app under each:
No additional post_install step is required for this SDK beyond what React Native already generates. After changing linkage, reinstall the pods:
cd ios && rm -rf Pods && pod install
Delete only Pods — keep Podfile.lock so a linkage change doesn't re-resolve and bump unrelated dependencies. Add --repo-update only if you also need to refresh the CocoaPods spec repo.
Configure the SDK
You need to make your Android, iOS or Expo applications aware that an authentication result will be received from the browser. This SDK makes use of the Android's Package Name and its analogous iOS's Product Bundle Identifier to generate the redirect URL. Each platform has its own set of instructions.
Android
Before version 2.9.0, this SDK required you to add an intent filter to the Activity on which you're going to receive the authentication result, and to use the singleTasklaunchMode in that activity. To migrate your app to version 2.9.0+, remove both and continue with the instructions below.
You can also check out a sample migration diff here.
Open your app's build.gradle file (typically at android/app/build.gradle) and add the following manifest placeholders:
android { defaultConfig { // Add the next line manifestPlaceholders = [auth0Domain: "YOUR_AUTH0_DOMAIN", auth0Scheme: "${applicationId}.auth0"] } ...}
The auth0Domain value must be replaced with your Auth0 domain value. So if you have samples.us.auth0.com as your Auth0 domain you would have a configuration like the following:
The applicationId value will be auto-replaced at runtime with the package name or ID of your application (e.g. com.example.app). You can change this value from the build.gradle file. You can also check it at the top of your AndroidManifest.xml file.
Note that if your Android application is using product flavors, you might need to specify different manifest placeholders for each flavor.
If you use a value other than applicationId in auth0Scheme you will also need to pass it as the customScheme option parameter of the authorize and clearSession methods.
Take note of this value as you'll be requiring it to define the callback URLs below.
If you don't plan to use Web Authentication, you will notice that the compiler will still prompt you to provide the manifestPlaceholders values, since the RedirectActivity included in this library will require them, and the Gradle tasks won't be able to run without them.
Re-declare the activity manually with tools:node="remove" in your app's Android Manifest in order to make the manifest merger remove it from the final manifest file. Additionally, one more unused activity can be removed from the final APK by using the same process. A complete snippet to achieve this is:
Forward incoming URLs to React Native so the login callback can be processed. Where to do that depends on your app's lifecycle.
React Native 0.88 and later use the UIScene lifecycle. Inside the ios folder find the file SceneDelegate.swift and add the following to it (new projects already include these methods):
If your application is generated using the React Native CLI, the default value of $(PRODUCT_BUNDLE_IDENTIFIER) matches org.reactjs.native.example.$(PRODUCT_NAME:rfc1034identifier). Take note of this value as you'll be requiring it to define the callback URLs below. If desired, you can change its value using XCode in the following way:
Open the ios/TestApp.xcodeproj file replacing 'TestApp' with the name of your app or run xed ios from a Terminal.
Open your project's or desired target's Build Settings tab and on the search bar at the right type "Product Bundle Identifier".
Replace the Product Bundle Identifier value with your desired application's bundle identifier name (e.g. com.example.app).
If you've changed the project wide settings, make sure the same were applied to each of the targets your app has.
If you use a value other than $(PRODUCT_BUNDLE_IDENTIFIER) in the CFBundleURLSchemes field of the Info.plist you will also need to pass it as the customScheme option parameter of the authorize and clearSession methods.
:warning: This SDK is not compatible with "Expo Go" app because of custom native code. It is compatible with Custom Dev Client and EAS builds
To use the SDK with Expo, configure the app at build time by providing the domain and the customScheme values through the Config Plugin. To do this, add the following snippet to app.json or app.config.js:
:info: If you want to switch between multiple domains in your app, refer here
API
Description
domain
Mandatory: Provide the Auth0 domain that can be found at the Application Settings
customScheme
Optional: Custom scheme to build the callback URL with. The value provided here should be passed to the customScheme option parameter of the authorize and clearSession methods. The custom scheme should be a unique, all lowercase value with no special characters. To use Android App Links, set this value to "https".
Note: When using customScheme: "https" for Android App Links, the plugin will automatically add android:autoVerify="true" to the intent-filter in your Android manifest to enable automatic verification of App Links.
Now you can run the application using expo run:android or expo run:ios.
Callback URL(s)
Callback URLs are the URLs that Auth0 invokes after the authentication process. Auth0 routes your application back to this URL and appends additional parameters to it, including a token. Since callback URLs can be manipulated, you will need to add this URL to your Application's Allowed Callback URLs for security. This will enable Auth0 to recognize these URLs as valid. If omitted, authentication will not be successful.
[!IMPORTANT]
Callback URL Formatting: Must be all lowercase, have no trailing slash, and exactly match the URL in Auth0 Dashboard. Incorrect formatting causes the app to "hang" after authentication. See FAQ #17 for troubleshooting.
On the Android platform this URL is case-sensitive. Because of that, this SDK will auto convert the Bundle Identifier (iOS) and Application ID (Android) values to lowercase in order to build the Callback URL with them. If any of these values contains uppercase characters a warning message will be printed in the console. Make sure to check that the right Callback URL is whitelisted in the Auth0 dashboard or the browser will not route successfully back to your application.
Go to the Auth0 Dashboard, select your application and make sure that Allowed Callback URLs contains the URLs defined below.
If in addition you plan to use the log out method, you must also add these URLs to the Allowed Logout URLs.
Replace {YOUR_APP_PACKAGE_NAME} and {YOUR_AUTH0_DOMAIN} with your actual application package name and Auth0 domain. Ensure that {YOUR_APP_PACKAGE_NAME} is all lowercase.
To enable App Links, set the auth0Scheme to https in your build.gradle file.
This configuration ensures that your app uses https for the callback URL scheme, which is required for Android App Links.
Enable Android App Links Support
Android App Links allow an application to designate itself as the default handler of a given type of link. For example, clicking a URL in an email would open the link in the designated application. This guide will show you how to enable Android App links support for your Auth0-registered application using Auth0's Dashboard.
Scroll to the bottom of the Settings page, and select Show Advanced Settings.
Select Device Settings, provide the App Package Name and the SHA256 fingerprints of your app’s signing certificate for your Android application, and select Save Changes.
You can use the following command to generate the fingerprint using the Java keytool in your terminal: keytool -list -v -keystore my-release-key.keystore
To learn more about signing certificates, see Android's Sign Your App developer documentation.
Replace {PRODUCT_BUNDLE_IDENTIFIER} and {YOUR_AUTH0_DOMAIN} with your actual product bundle identifier and Auth0 domain. Ensure that {PRODUCT_BUNDLE_IDENTIFIER} is all lowercase.
Expo
When using Expo, the callback URL format depends on whether you provide a customScheme in your app.json plugin configuration.
With customScheme
If you set a customScheme (e.g., "auth0sample") in your app.json:
Example: If your custom scheme is auth0sample, your Auth0 domain is example.us.auth0.com, your iOS bundle identifier is com.example.myapp, and your Android package name is com.example.myapp:
All values must be lowercase with no trailing slash.
Configure an associated domain for iOS
[!IMPORTANT]
This step requires a paid Apple Developer account. It is needed to use Universal Links as callback and logout URLs.
Skip this step to use a custom URL scheme instead.
Configure the Team ID and bundle identifier
Scroll to the end of the settings page of your Auth0 application and open Advanced Settings > Device Settings. In the iOS section, set Team ID to your Apple Team ID, and App ID to your app's bundle identifier.
This will add your app to your Auth0 tenant's apple-app-site-association file.
Add the associated domain capability
In Xcode, go to the Signing and Capabilitiestab of your app's target settings, and press the + Capability button. Then select Associated Domains.
Next, add the following entry under Associated Domains:
webcredentials:YOUR_AUTH0_DOMAIN
Example
If your Auth0 Domain were example.us.auth0.com, then this value would be:
webcredentials:example.us.auth0.com
If you have a custom domain, replace YOUR_AUTH0_DOMAIN with your custom domain.
[!NOTE]
For the associated domain to work, your app must be signed with your team certificate even when building for the iOS simulator. Make sure you are using the Apple Team whose Team ID is configured in the settings page of your Auth0 application.
This SDK is OIDC compliant. To ensure OIDC compliant responses from the Auth0 servers enable the OIDC Conformant switch in your Auth0 dashboard under Application / Settings / Advanced OAuth. For more information please check this documentation.
Web Authentication
The SDK exports a React hook as the primary interface for performing web authentication through the browser using Auth0 Universal Login.
Use the methods from the useAuth0 hook to implement login, logout, and to retrieve details about the authenticated user.
First, import the Auth0Provider component and wrap it around your application. Provide the domain and clientId values as given to you when setting up your Auth0 app in the dashboard:
If you're not using React Hooks, you can simply instantiate the Auth0 class:
import Auth0 from 'react-native-auth0';const auth0 = new Auth0({ domain: 'YOUR_AUTH0_DOMAIN', clientId: 'YOUR_AUTH0_CLIENT_ID',});
You can also pass custom headers that will be included in all API requests:
import Auth0 from 'react-native-auth0';const auth0 = new Auth0({ domain: 'YOUR_AUTH0_DOMAIN', clientId: 'YOUR_AUTH0_CLIENT_ID', headers: { 'X-Custom-Header': 'custom-value', },});
Then import the hook into a component where you want to get access to the properties and methods for integrating with Auth0:
import { useAuth0 } from 'react-native-auth0';
Login
Use the authorize method to redirect the user to the Auth0 Universal Login page for authentication. If scope is not specified, openid profile email is used by default.
The isLoading property is set to true once the authentication state of the user is known to the SDK.
The user property is populated with details about the authenticated user. If user is null, no user is currently authenticated.
The error property is populated if any error occurs.
Web Authentication flows require a Browser application installed on the device. When no Browser is available, an error of type a0.browser_not_available will be raised via the provided callback.
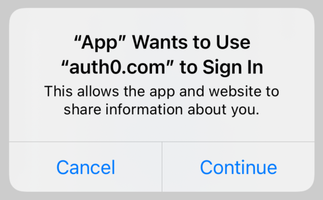
SSO Alert Box (iOS)
Check the FAQ for more information about the alert box that pops up by default when using Web Auth on iOS.
See also this blog post for a detailed overview of Single Sign-On (SSO) on iOS.
Logout
Log the user out by using the clearSession method from the useAuth0 hook.
The Credentials Manager allows you to securely store and retrieve the user's credentials. The credentials will be stored encrypted in Shared Preferences on Android, and in the Keychain on iOS.
The Auth0 class exposes the credentialsManager property for you to interact with using the API below.
💡 If you're using Web Auth (authorize) through Hooks, you do not need to manually store the credentials after login and delete them after logout; the SDK does this automatically.
Check for stored credentials
When the users open your app, check for valid credentials. If they exist, you can retrieve them and redirect the users to the app's main flow without any additional login steps.
const isLoggedIn = await auth0.credentialsManager.hasValidCredentials();if (isLoggedIn) { // Retrieve credentials and redirect to the main flow} else { // Redirect to the login page}
Retrieve stored credentials
The credentials will be automatically renewed using the refresh token, if the access token has expired. This method is thread safe.
💡 You do not need to call credentialsManager.saveCredentials() afterward. The Credentials Manager automatically persists the renewed credentials.
Requiring Authentication before obtaining Credentials
:warning: The requireLocalAuthentication method is no longer available as part of the CredentialsManager class or the useAuth0 Hook from v4 of the SDK.
ℹ️ You need to use at least version 0.59.0 of React Native, as it uses FragmentActivity as the base activity, which is required for biometric authentication to work.
You can enable an additional level of user authentication before retrieving credentials using the local authentication supported by the device, for example PIN or fingerprint on Android, and Face ID or Touch ID on iOS.
Refer to the instructions below to understand how to enable authentication before retrieving credentials based on your setup:
Using Auth0 Class:
The Auth0 class constructor now accepts a new parameter, which is an instance of the LocalAuthenticationOptions object. This needs to be passed while creating an instance of Auth0 to enable authentication before obtaining credentials, as shown in the code snippet below:
import Auth0 from 'react-native-auth0';const localAuthOptions: LocalAuthenticationOptions = { title: 'Authenticate to retrieve your credentials', subtitle: 'Please authenticate to continue', description: 'We need to authenticate you to retrieve your credentials', cancelTitle: 'Cancel', evaluationPolicy: LocalAuthenticationStrategy.deviceOwnerWithBiometrics, fallbackTitle: 'Use Passcode', authenticationLevel: LocalAuthenticationLevel.strong, deviceCredentialFallback: true,};const auth0 = new Auth0({ domain: config.domain, clientId: config.clientId, localAuthenticationOptions: localAuthOptions,});
Using Hooks (Auth0Provider):
Auth0Provider now accepts a new parameter, which is an instance of the LocalAuthenticationOptions object. This needs to be passed to enable authentication before obtaining credentials, as shown in the code snippet below:
import { Auth0Provider } from 'react-native-auth0';const localAuthOptions: LocalAuthenticationOptions = { title: 'Authenticate to retrieve your credentials', subtitle: 'Please authenticate to continue', description: 'We need to authenticate you to retrieve your credentials', cancelTitle: 'Cancel', evaluationPolicy: LocalAuthenticationStrategy.deviceOwnerWithBiometrics, fallbackTitle: 'Use Passcode', authenticationLevel: LocalAuthenticationLevel.strong, deviceCredentialFallback: true,};const App = () => { return ( <Auth0Provider domain={config.domain} clientId={config.clientId} localAuthenticationOptions={localAuthOptions} > {/* YOUR APP */} </Auth0Provider> );};export default App;
Detailed information on LocalAuthenticationOptions is available here
LocalAuthenticationOptions:
The options for configuring the display of local authentication prompt, authentication level (Android only), and evaluation policy (iOS only).
Properties:
Property
Type
Description
Applicable Platforms
title
String
The title of the authentication prompt.
Android, iOS
subtitle
String (optional)
The subtitle of the authentication prompt.
Android
description
String (optional)
The description of the authentication prompt.
Android
cancelTitle
String (optional)
The cancel button title of the authentication prompt.
Android, iOS
evaluationPolicy
LocalAuthenticationStrategy (optional)
The evaluation policy to use when prompting the user for authentication. Defaults to deviceOwnerWithBiometrics.
iOS
fallbackTitle
String (optional)
The fallback button title of the authentication prompt.
iOS
authenticationLevel
LocalAuthenticationLevel (optional)
The authentication level to use when prompting the user for authentication. Defaults to strong.
Android
deviceCredentialFallback
Boolean (optional)
Should the user be given the option to authenticate with their device PIN, pattern, or password instead of a biometric. Defaults to false. On iOS this is equivalent to setting evaluationPolicy to deviceOwner.
Android, iOS
:warning: You need a real device to test Local Authentication for iOS. Local Authentication is not available in simulators.
Error taxonomy
Every error the SDK throws extends AuthError. The six normalized subclasses below carry a
normalized, platform-agnostictype — switch on type, not code, for these and your error
handling behaves identically on iOS, Android, and web. Flows that throw a plain AuthError
instead — for example Custom Token Exchange, which surfaces
the raw OAuth error from the token endpoint — don't get a normalized type; there, code is the
correct (and only) thing to switch on.
Property
Use it for
type
Control flow for the six normalized subclasses. A normalized code, stable across platforms. Compare against the …ErrorCodes constants.
code
Diagnostics for the normalized subclasses (raw code from the underlying platform SDK or wire response, varies by platform); control flow for plain AuthError flows that have no normalized type.
message
Human-readable description. Not stable — do not parse it.
status
HTTP status, when the failure came from an HTTP response (0 otherwise).
Each of the six normalized classes ships a companion constants object and a matching TypeScript
union. Dropping the default branch is not enough for TypeScript to flag a missing case: a
switch that only has side effects compiles even when it skips a value, so a new error code would
be ignored silently. For a compile-time check, end the switch with a default that assigns the
value to never:
default: { const unhandled: never = error.type; // fails to compile if a case is missing throw new Error(`Unhandled error type: ${unhandled}`);}
The example below uses a plain fallback for brevity, so it does not get that check:
Error class
Constants
Type union
Thrown by
WebAuthError
WebAuthErrorCodes
WebAuthErrorCode
webAuth.authorize(), webAuth.clearSession()
CredentialsManagerError
CredentialsManagerErrorCodes
CredentialsManagerErrorCode
credentialsManager.*
MfaError
MfaErrorCodes
MfaErrorCode
mfa.*
PasskeyError
PasskeyErrorCodes
PasskeyErrorCode
passkey signup/login and passkey enrollment
MyAccountError
MyAccountErrorCodes
MyAccountErrorCode
myAccount.*
DPoPError
DPoPErrorCodes
DPoPErrorCode
getDPoPHeaders() and DPoP key handling
TimeoutError
—
type is always 'TIMEOUT_ERROR'
HTTP requests exceeding timeout
import { WebAuthError, WebAuthErrorCodes } from 'react-native-auth0';import type { WebAuthErrorCode } from 'react-native-auth0';function describe(type: WebAuthErrorCode): string { switch (type) { case WebAuthErrorCodes.USER_CANCELLED: return 'Cancelled'; case WebAuthErrorCodes.NETWORK_ERROR: return 'Offline'; default: return 'Login failed'; }}
Auth0ErrorCode is the union of all of the above. Prefer the specific union when handling one error
class — it keeps switch statements exhaustive and rejects codes that cannot occur there. Reach for
Auth0ErrorCode only in generic code such as logging or telemetry.
Stability. These constants, their unions, and the type values they contain are the public
error contract. Values will not be removed or renamed outside a major version.
MyAccountError is the one class with an extra property: the My Account API reports failures as
RFC 7807 type URIs, so type holds the normalized
code while typeUri preserves the original URI (e.g. https://auth0.com/api-errors/A0E-401-0001) for
logging and support tickets.
Credentials Manager errors
The Credentials Manager will only throw CredentialsManagerError exceptions. You can find more information in the details property of the exception.
SESSION_EXPIRED is raised when the upstream IdP session ceiling (IPSIE session_expiry claim) has been reached. The local session is no longer valid and the user must re-authenticate. See IPSIE Session Expiry for details.
MFA errors
All MFA operations (via auth0.mfa or the mfa property from useAuth0()) throw MfaError with a normalized type property:
import { MfaError, MfaErrorCodes } from 'react-native-auth0';try { const credentials = await auth0.mfa.verify({ mfaToken, otp: '123456' });} catch (error) { if (error instanceof MfaError) { switch (error.type) { case MfaErrorCodes.INVALID_OTP: console.log('Incorrect OTP code.'); break; case MfaErrorCodes.EXPIRED_MFA_TOKEN: console.log('MFA session expired. Please start over.'); break; case MfaErrorCodes.TOO_MANY_ATTEMPTS: console.log('Too many attempts. Please wait.'); break; case MfaErrorCodes.ENROLLMENT_FAILED: console.log('MFA enrollment failed.'); break; default: console.error('MFA error:', error.message); } }}
// Old way: required checking Platform.OS and different error codesimport { Platform } from 'react-native';try { await auth0.webAuth.authorize();} catch (e) { const isCancelled = Platform.OS === 'ios' ? e.code === 'USER_CANCELLED' : e.code === 'a0.session.user_cancelled'; if (isCancelled) { console.log('User cancelled the login.'); } else { console.error(e); }}
After (Platform-Agnostic and Typed)
// New way: use 'instanceof' and the 'type' propertyimport { WebAuthError } from 'react-native-auth0';try { await auth0.webAuth.authorize();} catch (e) { if (e instanceof WebAuthError && e.type === 'USER_CANCELLED') { console.log('User cancelled the login.'); } else { // Handle other errors console.error(e); }}
Using Error Code Constants (Recommended)
For better type safety and autocompletion, you can use the exported error code constants:
import { WebAuthError, WebAuthErrorCodes } from 'react-native-auth0';try { await auth0.webAuth.authorize();} catch (e) { if (e instanceof WebAuthError) { switch (e.type) { case WebAuthErrorCodes.USER_CANCELLED: console.log('User cancelled the login.'); break; case WebAuthErrorCodes.NETWORK_ERROR: console.log('Network error occurred. Please check your connection.'); break; case WebAuthErrorCodes.BROWSER_NOT_AVAILABLE: console.log('No browser available on this device.'); break; default: console.error('Authentication error:', e.message); } }}
Platform-Agnostic
Description
Android Native Error
iOS Native Error
Web Error Code
USER_CANCELLED
The user actively cancelled the web authentication flow.
a0.session.user_cancelled
USER_CANCELLED
cancelled
BROWSER_NOT_AVAILABLE
No compatible browser application is installed on the device.
a0.browser_not_available
-
FAILED_TO_LOAD_URL
The authorization URL could not be loaded in the browser.
a0.session.failed_load
-
BROWSER_TERMINATED
The browser was closed unexpectedly, likely because the application was relaunched from the home screen while the login was in progress.
a0.session.browser_terminated
-
INVALID_STATE
The state parameter returned from the server did not match the one sent, indicating a potential Cross-Site Request Forgery (CSRF) attack. Distinguished from ACCESS_DENIED by the native code being state_mismatch, or the error message containing state is invalid.
access_denied
access_denied
state_mismatch
ACCESS_DENIED
The user or Auth0 denied the authentication request. This can be caused by a user denying consent, a failing Action or Rule, or other authorization policies.
access_denied
access_denied
access_denied
CONSENT_REQUIRED
The user needs to explicitly grant consent for the application to access requested scopes or resources.
-
consent_required
INVALID_CONFIGURATION
The Auth0 Application is misconfigured. Common causes include an invalid social connection configuration.
a0.invalid_configuration
a0.invalid_configuration
PKCE_NOT_ALLOWED
PKCE is required but not enabled for the Auth0 Application. Ensure the "Application Type" is set to "Native" in your Auth0 dashboard.
a0.pkce_not_available
-
ID_TOKEN_VALIDATION_FAILED
The ID token received is invalid and failed one or more validation checks, such as signature, issuer, audience, or nonce verification.
a0.session.invalid_idtoken
ID_TOKEN_VALIDATION_FAILED
(various validation Errors).
INVALID_CALLBACK_URL
The URL that returned to the app did not match the expected callback. On iOS this commonly happens when an in-page link (e.g. a privacy-policy link) reuses the app's custom scheme and is captured by ASWebAuthenticationSession instead of the real callback. Keep your configured callback in the required format and ensure such in-page links use https:// rather than the app's custom scheme.
-
INVALID_CALLBACK_URL
AUTHENTICATION_FAILED
The callback URL carried an error that could not be attributed to a more specific cause. iOS only.
-
AUTHENTICATION_FAILED
CODE_EXCHANGE_FAILED
Exchanging the authorization code for tokens failed. iOS only.
-
CODE_EXCHANGE_FAILED
NETWORK_ERROR
A network error occurred, preventing the request from completing. The device may be offline or unable to reach the Auth0 servers.
a0.network_error
OTHER (with URLError cause)
(Network-related fetch exception)
TIMEOUT_ERROR
The web authentication flow timed out.
-
-
timeout (from PopupTimeoutError)
UNKNOWN_ERROR
An unexpected or uncategorized error occurred. Check the message and cause properties for more specific details.
(various)
UNKNOWN or OTHER
Features and Platform Support
This library provides a unified API across Native (iOS/Android) and Web platforms. However, due to security models and underlying technology, not all features are av